Installing a CMP is often one of the most visible actions when working on a website’s compliance. The banner appears, visitors can accept or reject and the project immediately feels like it has moved forward.
It is then tempting to summarize the situation as “the website has a CMP, so it is GDPR compliant”.
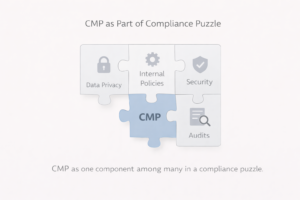
That shortcut is incorrect. A CMP can solve an important part of the problem, but that part remains only one component among many others.
This is also why I have never presented tarteaucitron as a tool capable of making an entire website GDPR compliant.
A CMP has a relatively precise role
A CMP primarily intervenes when a website uses technologies whose operation requires a user choice.
It can display information and a consent interface, remember choices required for its operation and make the use of certain services conditional on those choices.
With tarteaucitron, the core function is mainly controlling the loading of third-party services.
If YouTube needs to wait for consent, its iframe can be blocked. If Google Analytics must not operate before the visitor’s choice, its loading can be made conditional. If the visitor rejects it, that rejection must be respected.
This is already an important role, but its scope can be clearly identified.
The GDPR is not only about cookies
A website can process personal data without using a single advertising cookie.
A contact form collects a name, email address and sometimes a phone number. An online store stores order information and delivery addresses. A newsletter manages a subscriber list. Server logs may contain IP addresses.
A CMP does not decide how long those data should be retained, who can access them or how a data subject request should be handled.
These issues exist independently from the consent banner.
A CMP cannot magically write an accurate privacy policy
Some solutions provide policy generators. They can help prepare a document, but they cannot automatically know every internal processing activity within an organization.
A privacy policy needs to reflect how the website and organization actually operate.
If data from a form is copied into a CRM, transmitted to a provider and then retained for five years, the cookie banner has no intrinsic knowledge of that chain.
A CMP therefore cannot certify that information provided to individuals is complete for every processing activity.
It does not manage website security either
The GDPR also includes obligations relating to personal data security.
Installing an excellent CMP does not fix an outdated WordPress installation, a weak administrator password, a publicly exposed backup or a database accessible to an unauthorized third party.
Hosting, account, backup, application and data exchange security form another area of work.
The banner can be perfectly configured while the rest of the website has entirely unrelated problems.
A CMP does not select appropriate processors
Choosing and managing providers is another broader issue.
An organization may use a European CMP while sending form, customer or employee data to various external providers.
Contracts, respective roles, data transfers and associated safeguards need to be considered for each relevant processing activity.
The nationality of the CMP obviously cannot solve these questions for every other tool used by the website.
Even within its own scope, a CMP can be incorrectly installed
There is an even more fundamental difficulty: having a CMP does not necessarily mean that it performs its own role correctly.
If Google Analytics loads directly in the <head> before the CMP, subsequently displaying a banner cannot undo requests that have already been sent.
If a service is missing from the configuration, it may continue operating independently from the choices displayed to the visitor.
If Google Tag Manager triggers tags that are not properly conditioned, simply adding GTM to a CMP does not automatically solve the problem.
This is why technical verification of actual blocking matters much more than the visual presence of a banner.
Consent itself must be valid
Blocking scripts is not enough if the consent interface is misleading.
Consent needs to be freely given and result from a genuine choice. Accepting should not be significantly easier than rejecting.
A huge colorful “Accept all” button combined with a rejection option deliberately hidden behind several screens therefore creates a problem that technical sophistication cannot compensate for.
Interface design is part of the consent mechanism.
The website configuration evolves
Compliance checked on installation day does not remain frozen forever.
A WordPress plugin may add a new service. A marketing team may install a pixel. An external video may be embedded on a new page. A Google Tag Manager configuration may change without any visible modification to the website code.
The CMP therefore needs to follow the website’s actual evolution.
This is one reason why scanning, audits and regular verification can remain useful even when a CMP is already installed.
Choosing the legal basis is not the CMP’s job
Not all personal data processing relies on consent.
Depending on the processing activity, other legal bases may be relevant. A CMP is not a legal engine capable of automatically deciding which basis applies to every activity within an organization.
Even for trackers, some strictly necessary technologies may be exempt from prior consent under certain conditions.
The French data protection authority, for example, identifies trackers necessary for authentication, shopping carts and certain expected interface customizations among situations that may qualify for an exemption. Configuration therefore needs to reflect the actual use of a tracker rather than simply its name.
What can a good CMP actually guarantee?
I prefer to talk about technical capabilities rather than a global compliance guarantee.
A good CMP should make it possible to properly present choices relating to the services it manages, respect rejection, load relevant services only at the appropriate time and allow visitors to change their choice.
It should also be reliable enough to integrate so that those rules are actually enforced.
That is already a lot. But it does not cover forms, customer files, retention periods, security or contracts with providers.
Be careful with “automatic compliance” promises
I would therefore be cautious about a solution promising to make a website “100% GDPR compliant” simply by installing a script.
A tool can automate certain tasks, detect technologies, produce documents or simplify consent collection. It can save a considerable amount of time.
But it does not necessarily know about processing performed outside the browser or the organization’s internal processes.
The broader the compliance promise, the more important it is to examine precisely what is actually covered.
A CMP remains an important component
Saying that a CMP cannot guarantee complete compliance does not mean that it is secondary.
On a website using many third-party services, controlling what loads before the visitor’s choice can be significant technical work. A CMP exists precisely to centralize and make that part manageable.
I therefore consider tarteaucitron a specialized tool: it manages a specific problem rather than pretending to supervise an organization’s entire GDPR compliance.
When choosing a CMP, I prefer a solution that clearly explains its limits over one that promises to make such a broad subject disappear with a single JavaScript tag.